

Kenya’s digital ecosystem faces relentless cyber threats, with over 3.3 billion threat events detected in early 2026 alone. While ransomware and database exfiltrations dominate headlines, the majority of attacks begin quietly with Initial Access Brokers (IABs). Infostealers like Aotera, AgentTesla, and Vidar harvest corporate credentials from employees, contractors, or third-party vendors. These domain logins are bundled and sold on underground forums for as little as KES 2,000 to KES 15,000 ($15–$100).
Once an attacker purchases valid domain credentials, traditional endpoint defenses (EDR) and firewalls become blind because to the system, the attacker looks like a legitimate employee logging into Office 365, a VPN, or an internal HR portal.
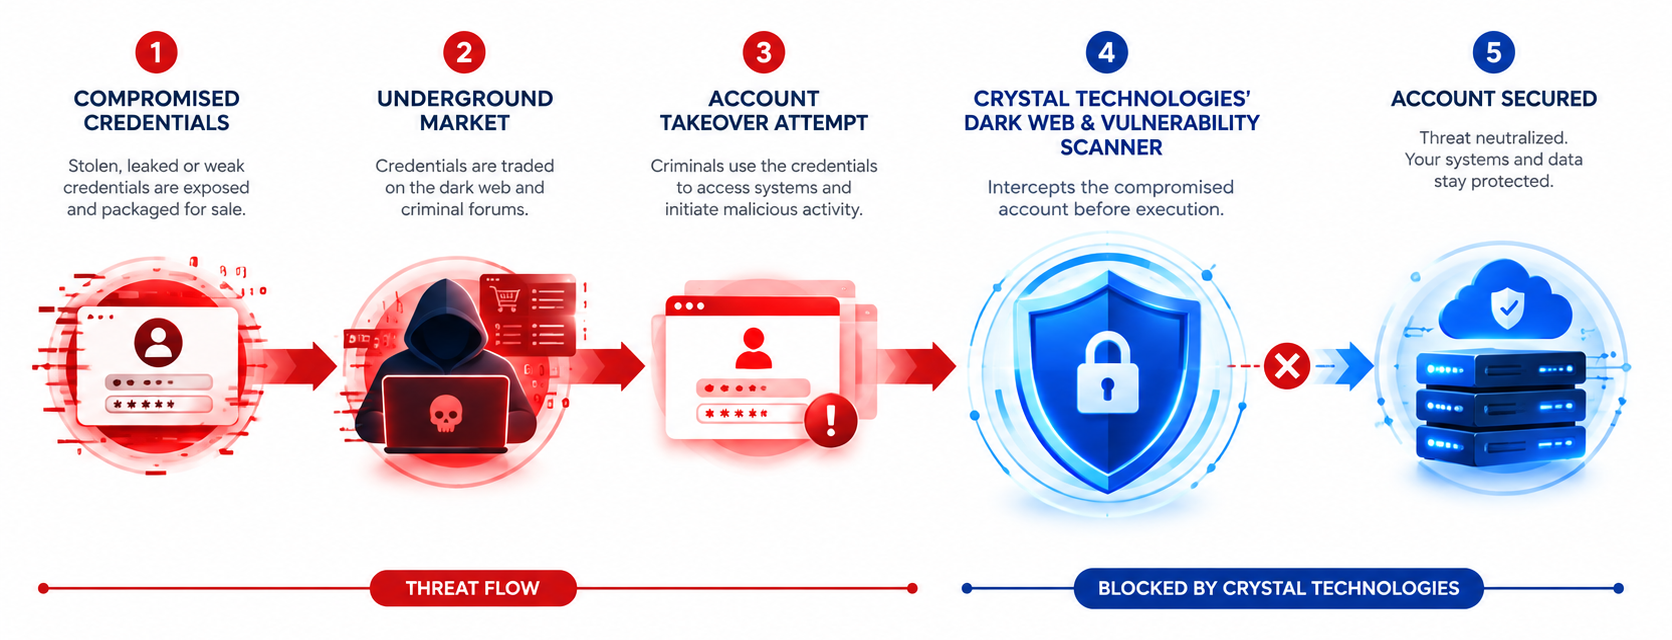
How Attackers Exploit Compromised Domain Credentials.
- Infostealer Infection: An employee uses an unpatched browser or personal laptop infected with malware. Session cookies, saved passwords, and corporate domain logins (
@company.co.ke) are harvested. - Underground Sale: The credentials surface on dark web marketplaces or encrypted Telegram channels within 24 to 72 hours.
- Reconnaissance & Weaponization: Threat actors cross-reference the leaked domain with public-facing vulnerabilities (e.g., exposed remote desktop endpoints or unpatched web applications).
- Execution: The attacker logs in bypassing basic perimeter defenses, moving laterally to deploy ransomware or exfiltrate customer databases.
Comparative Breakdown: Traditional Security vs. Proactive Credential & Vulnerability Scanning.
| Feature | Reactive Traditional Security | Proactive Dark Web & Vulnerability Scanning |
| Detection Point | Post-exploitation (Active intrusion/Alerts) | Pre-execution (Underground markets & dark web) |
| Visibility | Internal corporate network & endpoints | External dark web, paste sites, Telegram, & public attack surfaces |
| Identity Protection | Focuses on active brute-force attempts | Detects legitimate, exposed email/password pairs in real time |
| Vulnerability Mapping | Periodic internal scans | Continuous external attack surface mapping for exposed domain endpoints |
| Actionable Metric | Mean Time to Detect (MTTD) | Time to Invalidate Credential (TTIC) prior to breach |
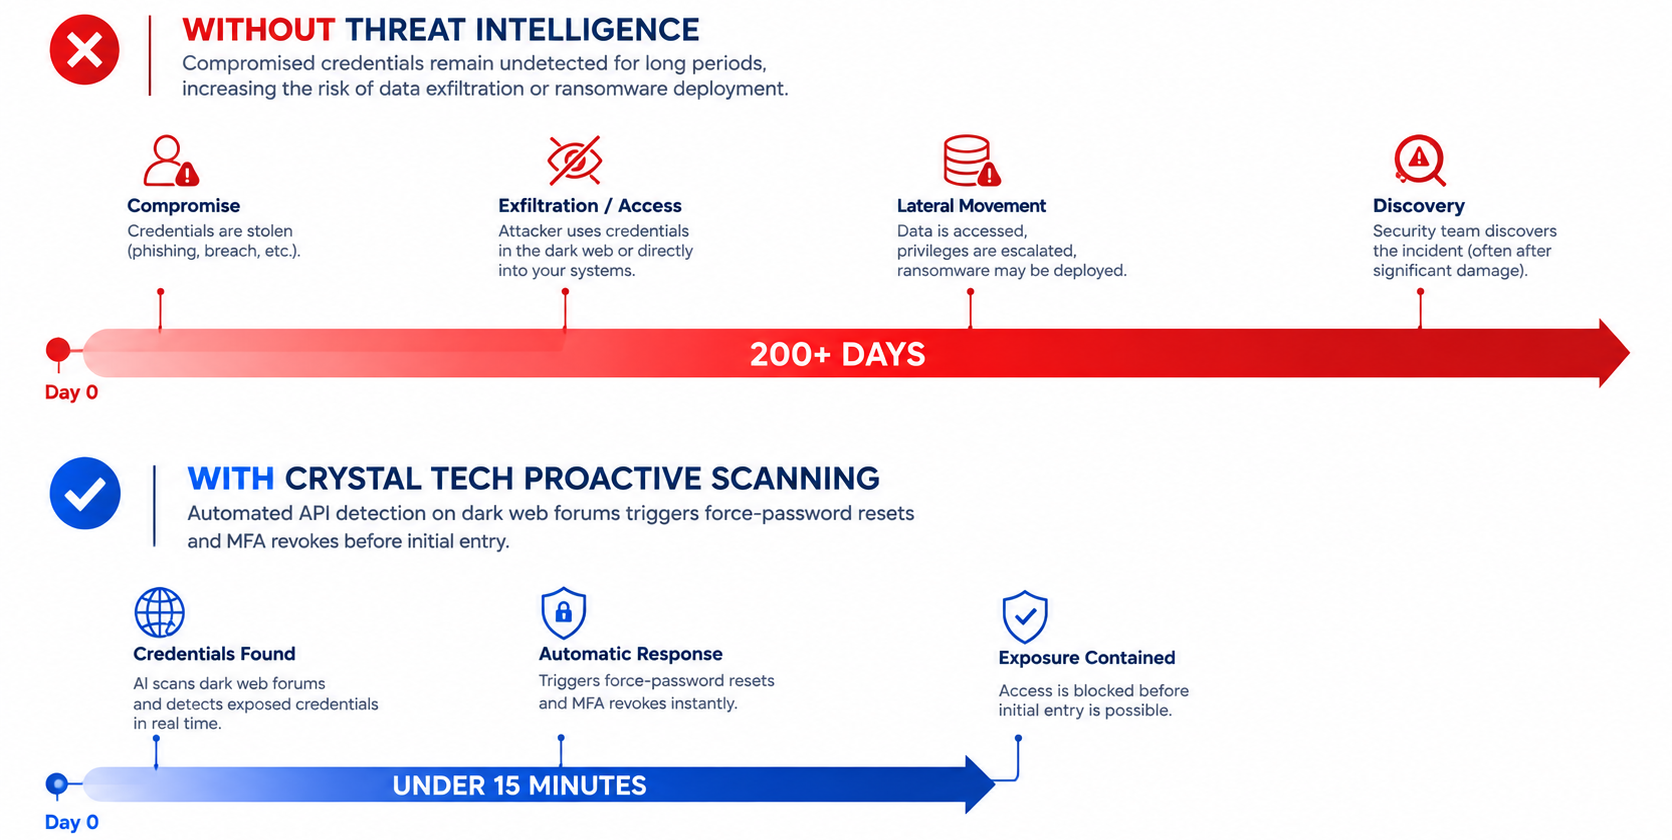
Stopping the Breach Before Execution.
Detecting compromised credentials requires going beyond corporate borders. Crystal Technologies integrates continuous dark web surveillance with automated external vulnerability scanning:
- Dark Web Surveillance: Continuous monitoring of dark web forums, paste sites, and closed messaging groups for exposed
@organization.co.kedomain credentials. - Attack Surface Management: Automated scanning of public-facing IPs, open RDP ports, and vulnerable web components matching your enterprise domain.
- Automated Remediation Workflows: Immediate triggering of force-password resets, active session termination, and step-up Multi-Factor Authentication (MFA) enforcement upon detection.
 Chat with Us